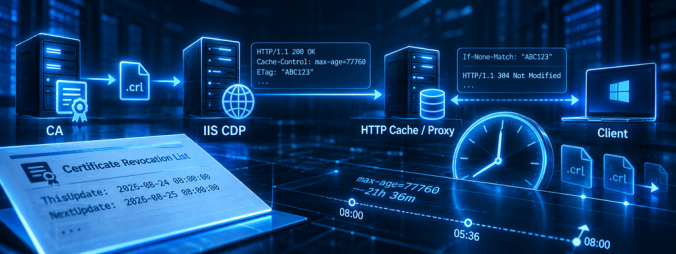
And we’re back again! During PKI assessments, I regularly come across IIS servers that are used as HTTP distribution points for CRLs and CA certificates. Most of the time, the web server itself works perfectly fine. The files are there, they can be downloaded, and certificate validation succeeds. There is, however, one configuration item that I see missing surprisingly often, HTTP caching. And when caching is configured, I regularly find values that do not match the CRL publication schedule. A common example is a cache lifetime of several days while the same web server is also distributing delta CRLs that are published every 24 hours.
Continue readingTag: Caching
Archives
- September 2026
- August 2026
- July 2026
- June 2026
- May 2026
- April 2026
- March 2026
- February 2026
- January 2026
- December 2025
- November 2025
- October 2025
- May 2025
- April 2025
- March 2025
- February 2025
- June 2024
- April 2024
- February 2024
- January 2024
- December 2023
- October 2023
- September 2023
- August 2023
- July 2023
- June 2023
- May 2023
- April 2023
- February 2023
- December 2022
- November 2022
- October 2022
- September 2022